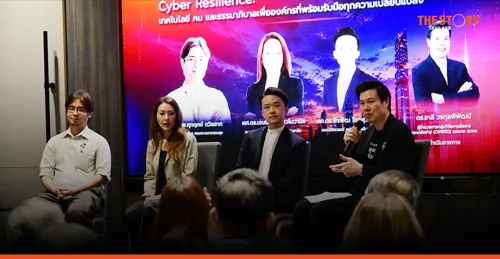
Cyber resilience reframes organizational security strategy from prevention to rapid recovery and business continuity. The article emphasizes that 100% security is impossible; instead, organizations must prioritize risks, balance security with usability, conduct regular cyber drills with leadership participation, and integrate governance, process, and human behavior—not just technology. This shift aligns with PDPA compliance requirements and reflects real-world constraints SMEs face: legacy systems, budget limits, and accidental data breaches from human error rather than sophisticated attacks.
← Back to all articles